Will The Police Ever Catch Your Attacker?
Find Threat Talks on


Most incident response plans assume a breach report ends with someone in handcuffs.
Stan Duijf, Head of Operations at the NIS of the Dutch National Police, says arrests are the wrong metric: his team measures how expensive they make crime to run.
Stan talks with Lieuwe Jan Koning, Co-founder & CTO at ON2IT, to explain why. A single investigation can span 5 to 20 countries, and many suspects live where an arrest isn’t possible. So the police work the economics instead. Operation Endgame hits the infrastructure attackers use to get in, twice a year.
Servers get seized, 35 million euros in crypto has been confiscated, and suspects land on sanctions and most-wanted lists. Arrests still happen, often the moment a suspect travels. If you’ve ever wondered what happens after you call the police, this is the conversation to have before the next breach, not after.
What you’ll learn
- Arrests are the wrong metric. Stan’s team measures disruption: how much more it costs criminals to operate.
- One case, up to 20 countries. Jurisdiction, language, and legislation all have to line up before anyone can act.
- Your threat intel matters to the police. Stan says exactly what he wants from a security team, and why.
Your cybersecurity experts
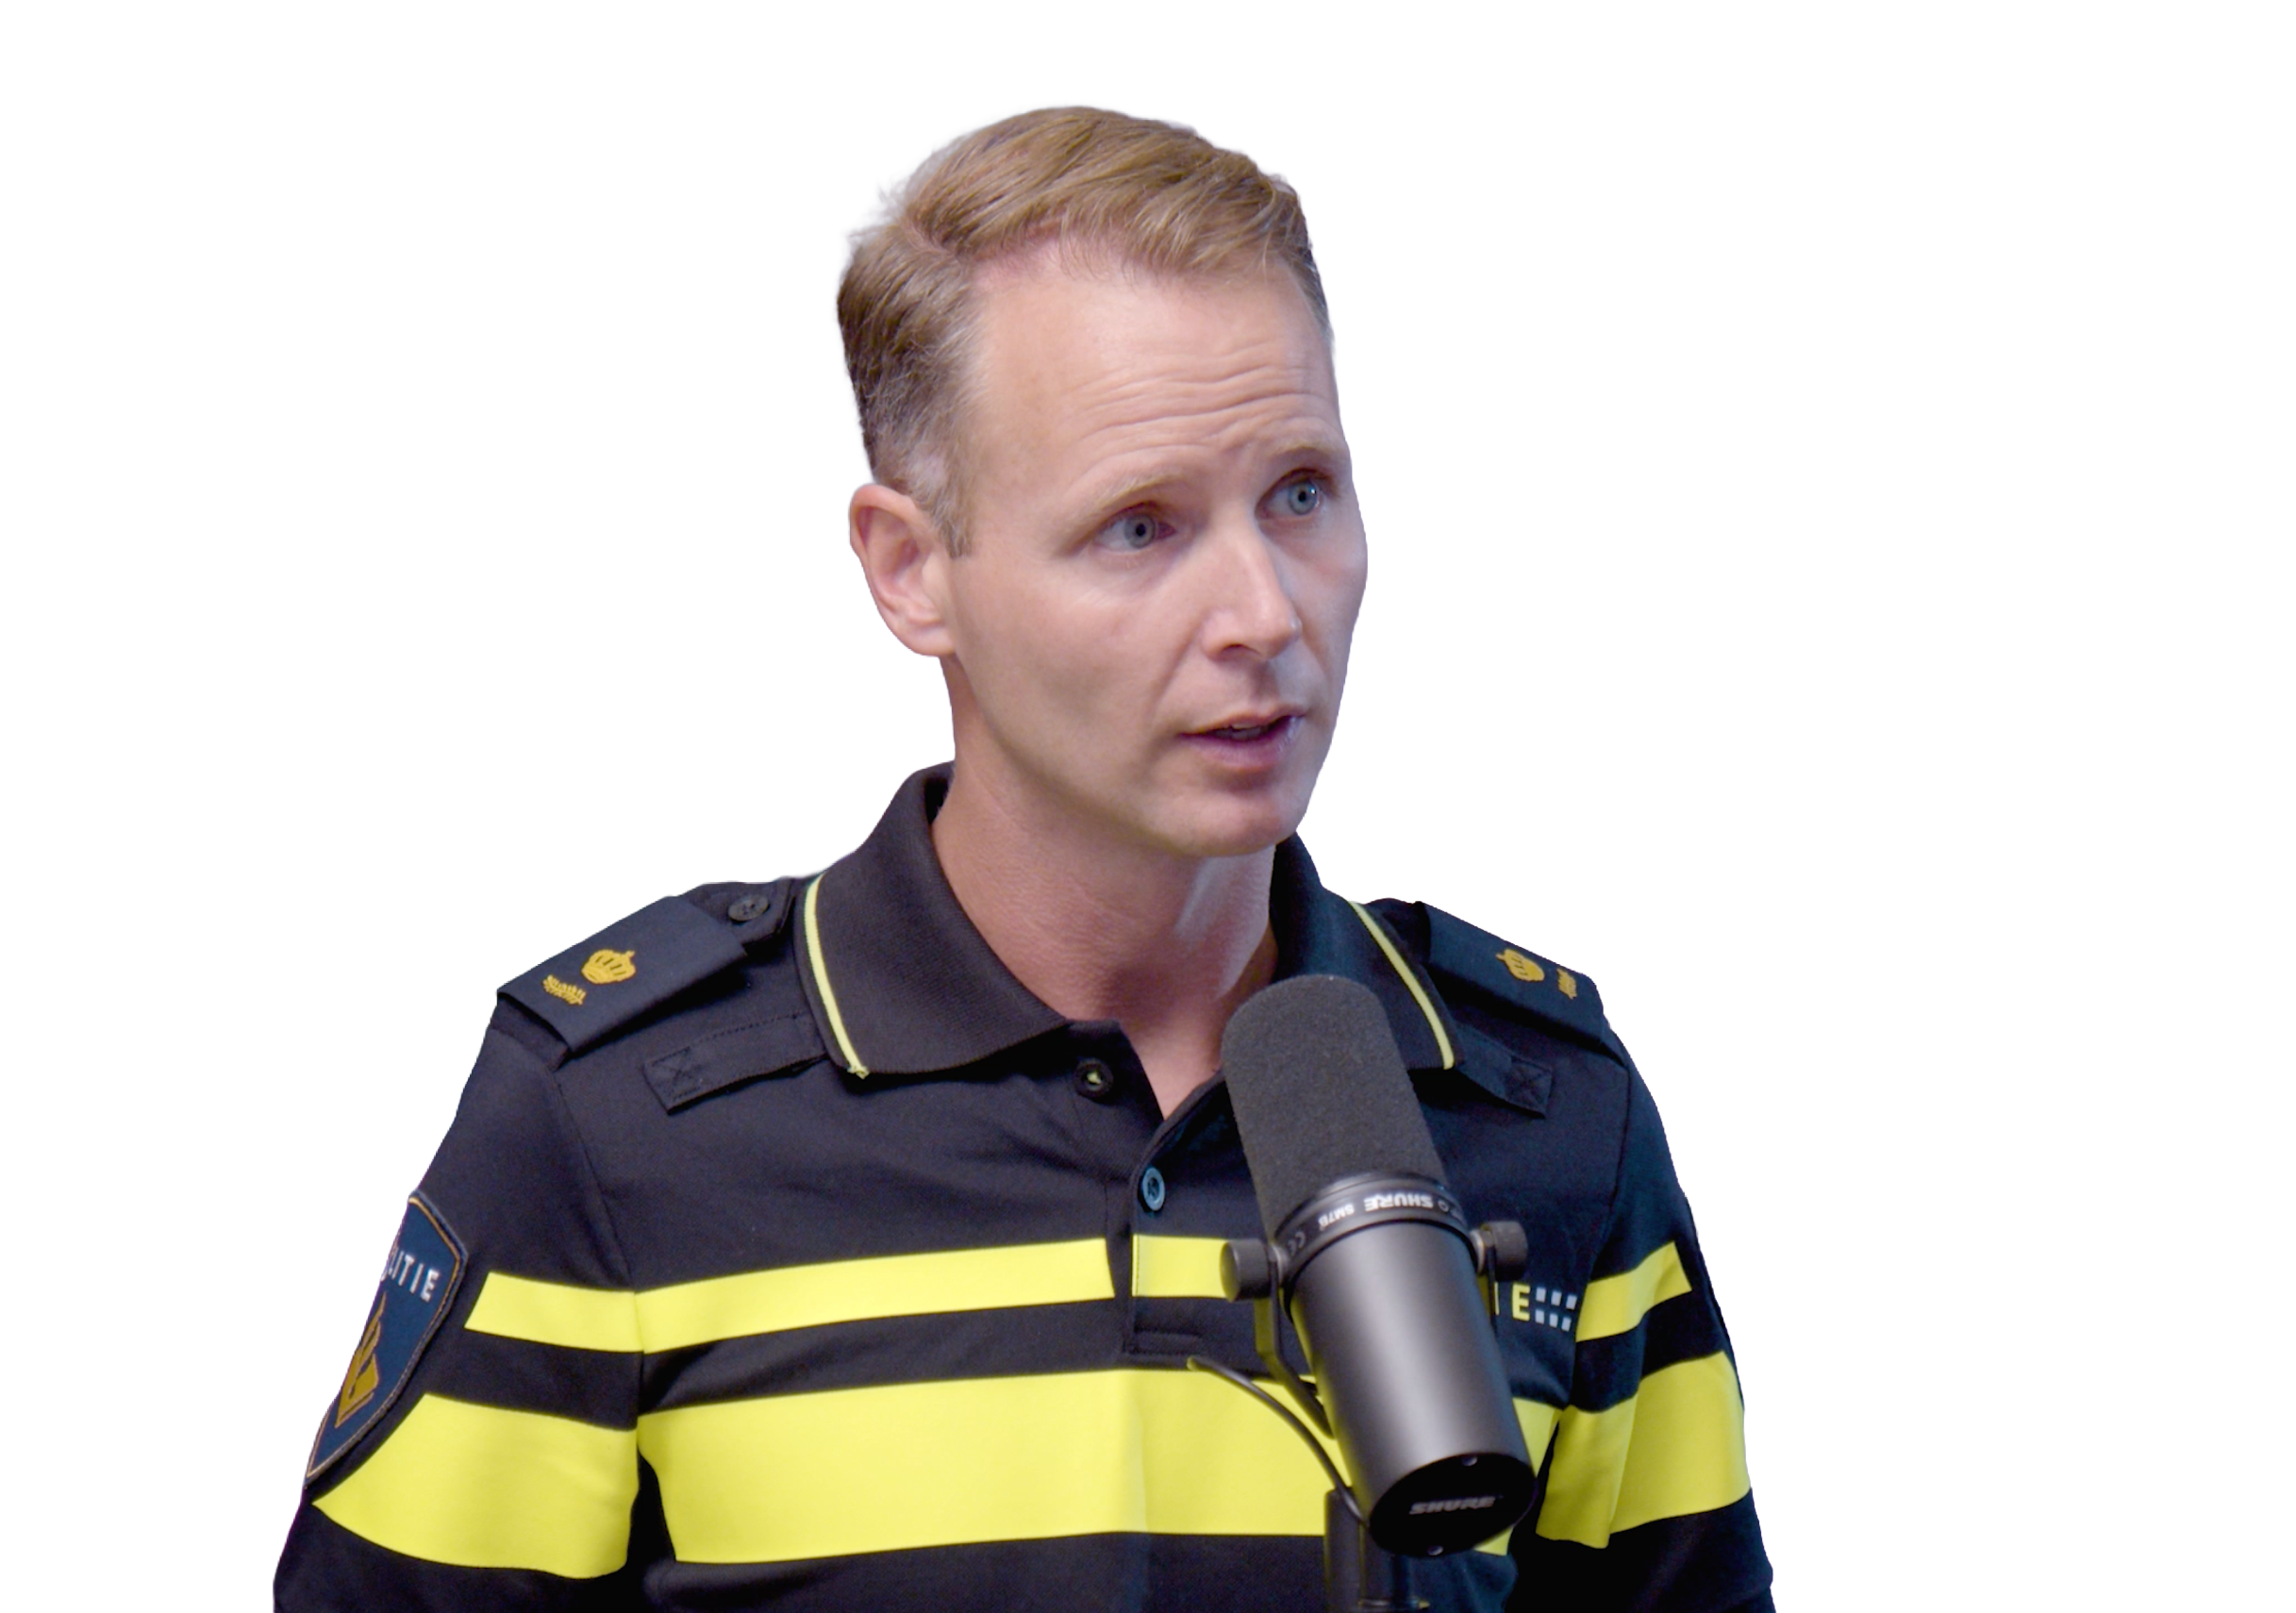
Stan Duijf
Head of operations – National Investigations and Special Operations (NIS),
National Police of the Netherlands
Rob Maas
Field CTO ON2IT
Episode details
Most security leaders carry a quiet assumption into every incident response plan: report the breach, and somewhere an investigator starts building a case against the person who did it. Stan Duijf’s answer is more honest than that. A typical cybercrime investigation touches 5 to 20 countries at once, each with its own laws and language, and infrastructure, victims, and offenders rarely sit in the same jurisdiction. By the time that aligns, the attacker has often moved on. Stan’s response isn’t resignation. It’s a different strategy.
That strategy is Operation Endgame, a campaign run with the Dutch police’s most trusted international partners, Germany among them. Rather than waiting for a single incident, the team intervenes in the criminal ecosystem twice a year, usually at the initial-access stage: info stealers, botnets, the infrastructure that gets an attacker in the door. For each intervention they ask which partner country holds the best legal cards, and play them together. It’s less a manhunt than a running campaign against a supply chain.
For organizations, the opening is threat intel, and Stan is specific about it. He wants knowledge of how a criminal group operates, how the ecosystem around it works, and concrete IP addresses tied to an active attack. He also describes a push toward integrated operations, where companies like Microsoft, Palo Alto Networks, and Google act inside their own networks alongside the police’s legal interventions. The Netherlands’ role as a hosting hub cuts both ways: it gives the police unusually direct access to infrastructure, and gives criminals an unusually fast pipe to hide behind.
The police raise the attacker’s cost from the outside. Zero Trust raises it from the inside, so a breach stays in one room. In the next episode, Stan and Lieuwe Jan cover what organizations can and can’t do after a breach, and what helps or hinders a police investigation.
Get your Hacker T-shirt
Join the treasure hunt!
Find the code within this episode and receive your own hacker t-shirt for free.
