Threat Talks
Recent Episodes
Lapsus$: How Teenagers Beat Microsoft, NVIDIA and Okta
Find Threat Talks onA group of teenagers breached Microsoft, NVIDIA and Okta. They used no zero-days, no custom malware, and no command and control infrastructure. They bought leaked credentials on the dark web, or called the service desk and asked for a password...
How a 19-Year-Old Hacked the NEWS Without Breaking In
Find Threat Talks onYour Outlook account recovery will accept an authenticator code on its own. No password, no inbox, no phone number. Whoever holds that TOTP secret owns the account, and the second factor you bought to survive credential theft becomes the only thing...
The End of Reactive Security
Your MDR detects known threats but does not block them. Lieuwe Jan Koning and Nicholai Piagentini on preemptive cybersecurity and the future of MDR.
NIST CSF 2.0: No CISO, No Excuse
Find Threat Talks onThe framework changed, but the question did not: what do I do tomorrow? NIST released version 2.0 of the Cybersecurity Framework, and for most teams the hard part is not the document, it is the first move. This episode is about that first move....
Your SOC Won’t Survive AI Attackers Without This Shift
Find Threat Talks onYour SOC Won't Survive AI Attackers Without This Shift Running a SOC was always hard. With AI in attackers' hands, hard becomes impossible, unless you change how you work. Open-source tools now find and exploit a flaw in about 15 minutes, with no...

Shiny Hunters: One Name Behind a Dozen Mega-Breaches
Find Threat Talks on Shiny Hunters: One Name Behind a Dozen Mega-Breaches Salesforce, Google, Okta, Louis Vuitton, Allianz, Odido: all breached under the same name. Shiny Hunters may not even be one group. It is a brand that different criminal crews borrow to...
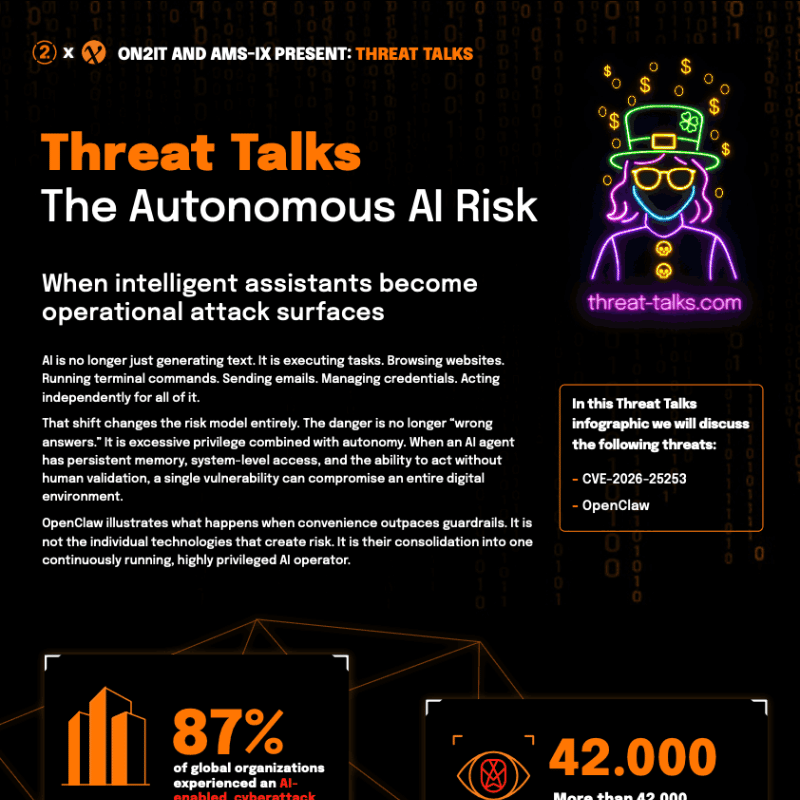
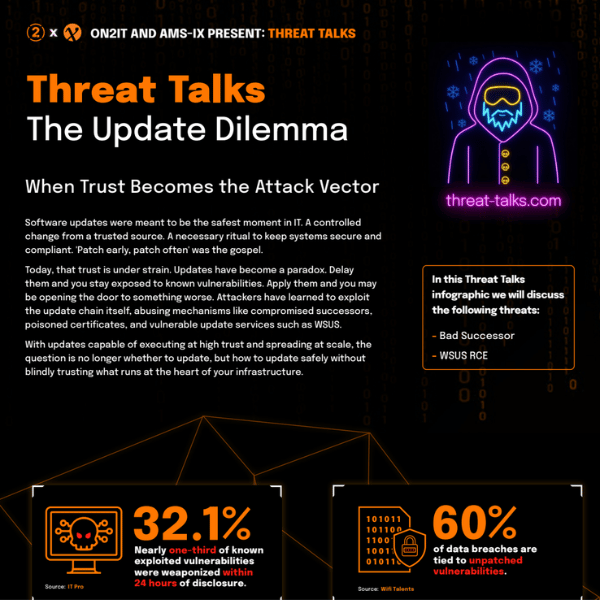
Cybersecurity Infographics
JOIN THE CYBERSECURITY CONVERSATION
Subscribe to Threat Talks for in-depth explorations of recent cybersecurity threats and trends, with exclusive insights and expert perspectives.


