When to call the Police after you’re hacked
Find Threat Talks on


You’ve been hacked. Who do you call first: your lawyer or the police?
Most companies call the lawyer. Stan Duijf, Head of Operations at the NIS of the Dutch National Police, explains to Lieuwe Jan Koning, Co-founder & CTO at ON2IT, why that order is costly. Only one in five of the 150+ data breaches reported in the Netherlands each year ever reaches the police, and the people whose data leaked pay for that gap as much as the company does.
What you’ll learn
- When a breach is serious enough to call the police, and why company size has nothing to do with it.
- Why paying a ransom never makes your data safe, even when the criminals hand it back.
- What to decide before you’re hacked, so you’re not deciding it in the first hours of a breach.
Your cybersecurity experts
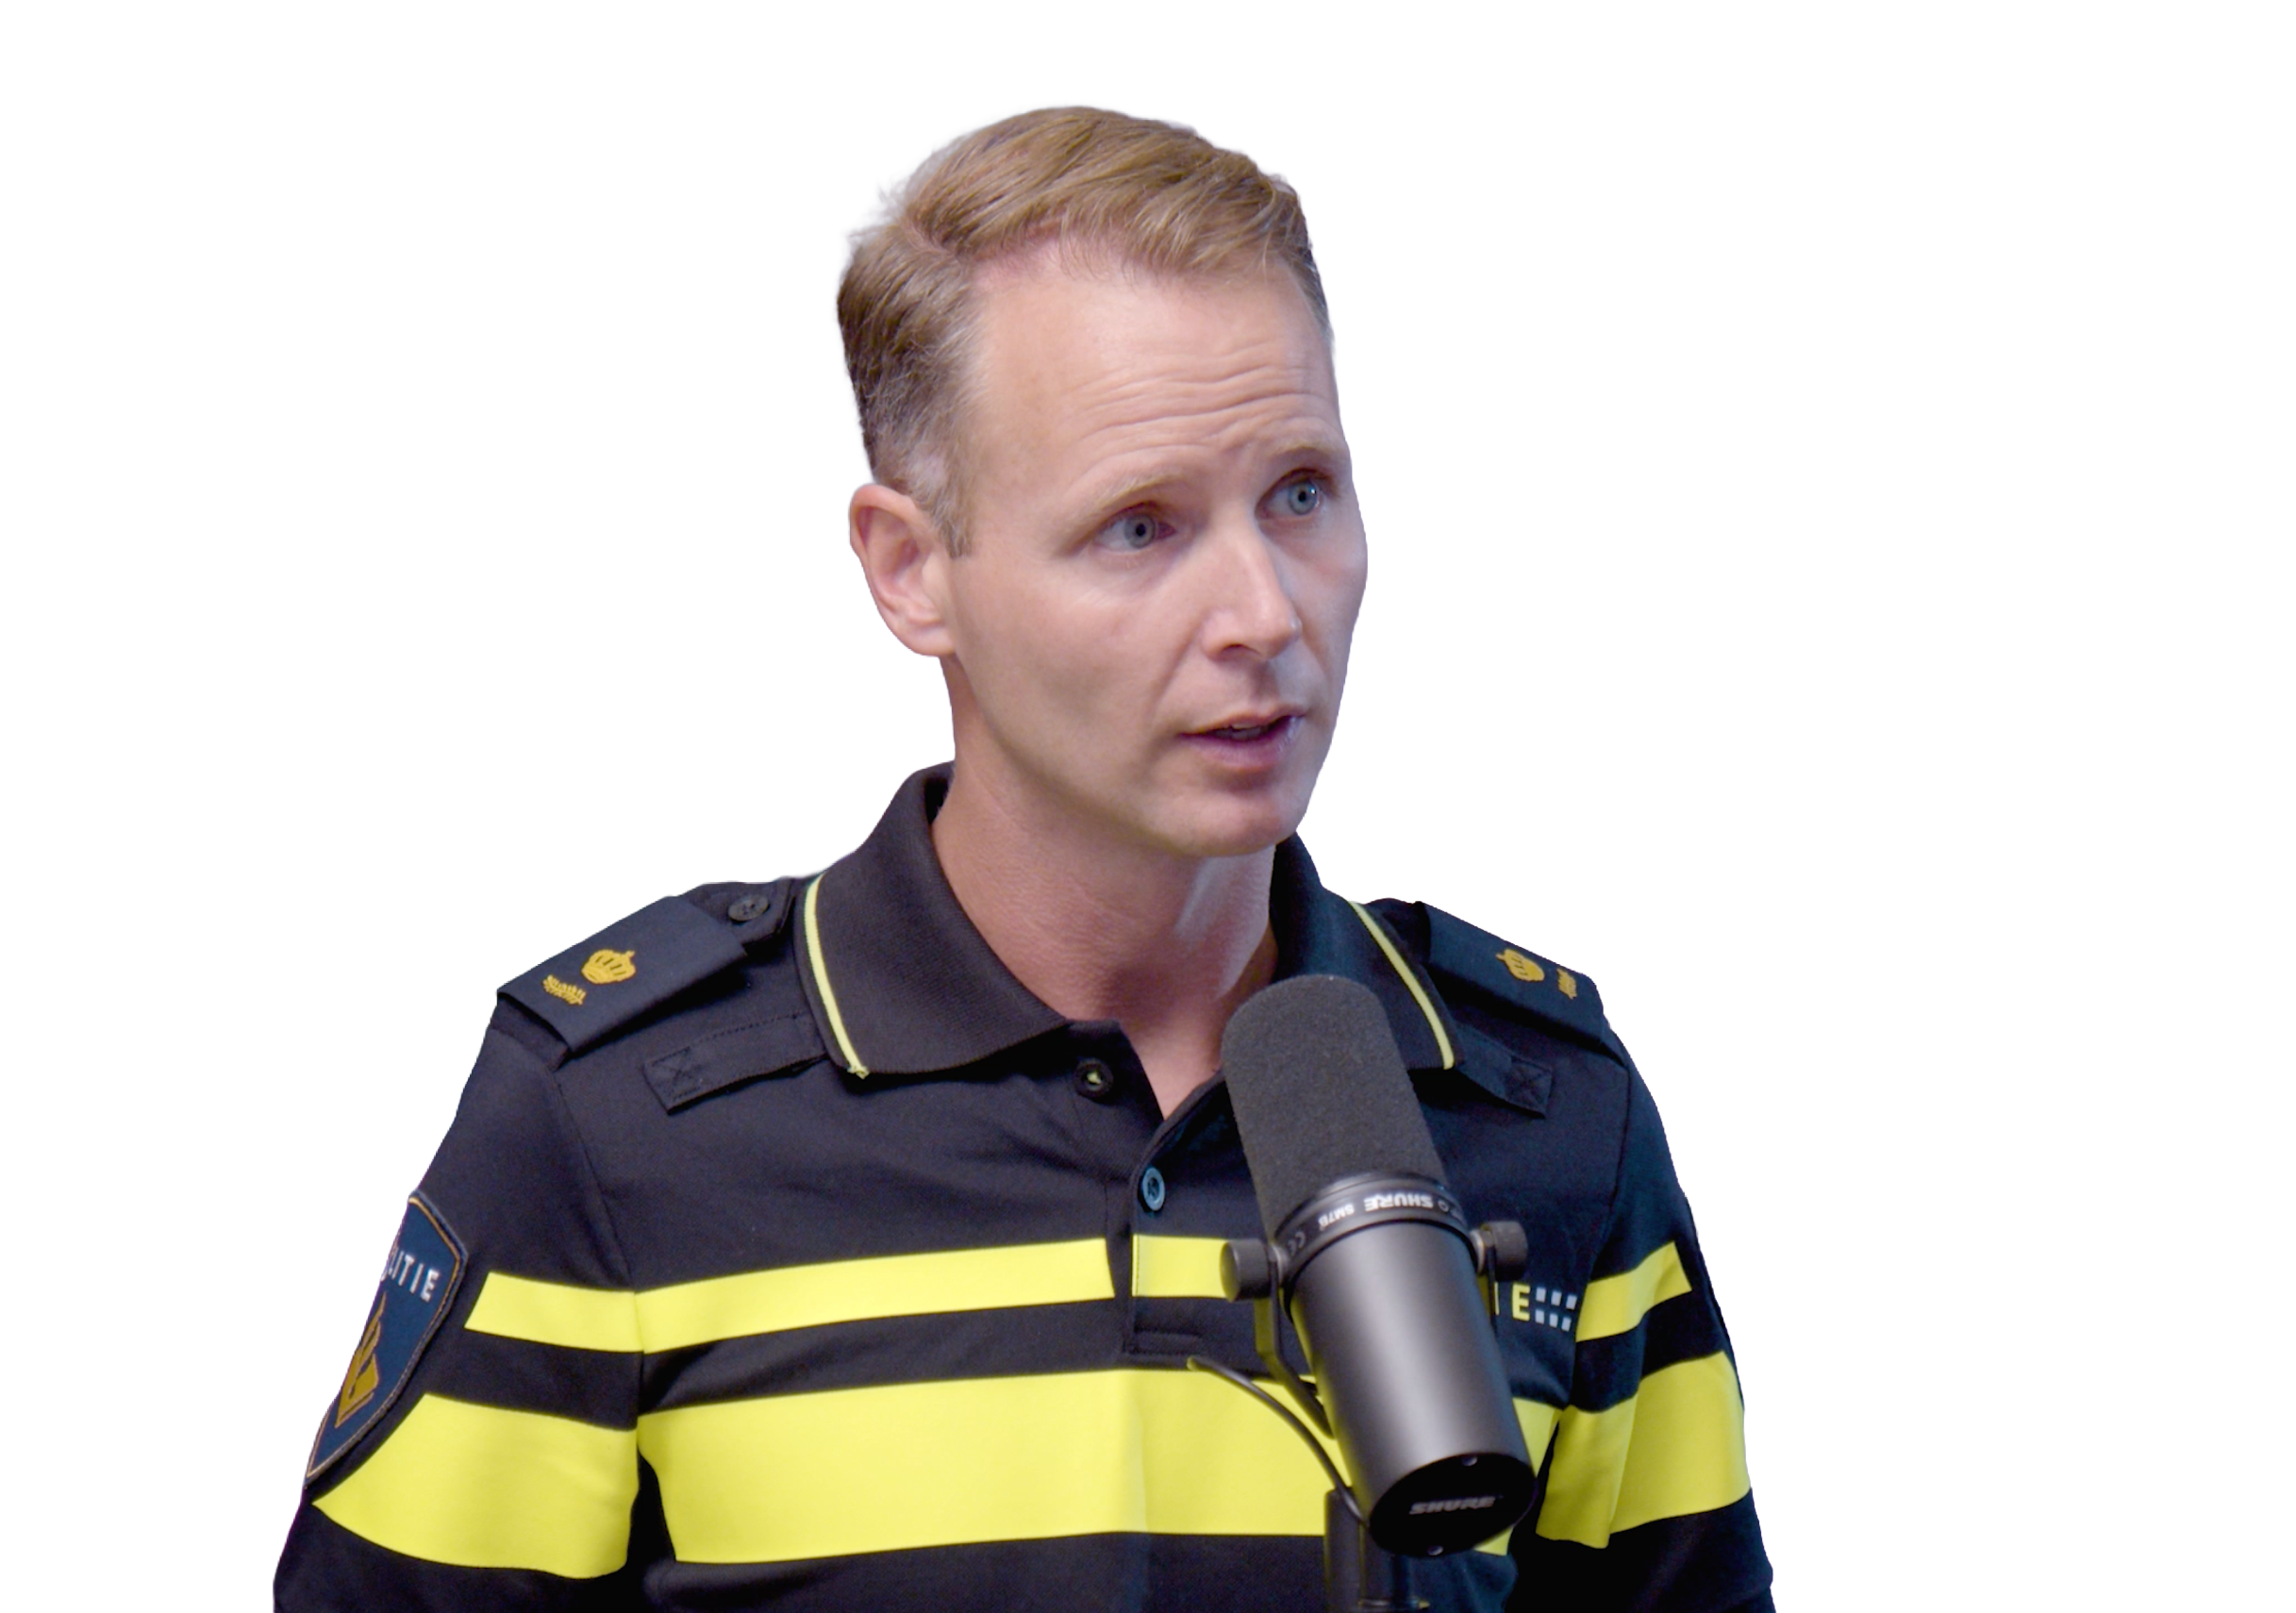
Stan Duijf
Head of operations – National Investigations and Special Operations (NIS),
National Police of the Netherlands
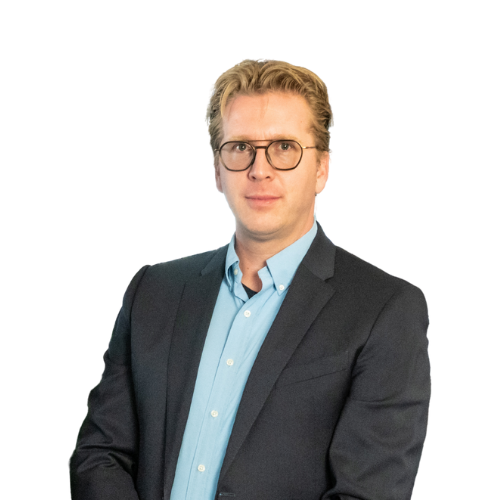
Rob Maas
Co-Founder and CTO ON2IT
Episode details
Most incident response plans have a line for forensics and a line for the lawyers. Very few have a line for the police. Of the roughly 150 data breaches reported in the Netherlands each year, only one in five reaches Stan Duijf’s unit, and most of those arrive too late to matter.
Timing matters because it decides what the police can still do. Called in early, they can join ransom negotiations, trace stolen cryptocurrency and build the forensic basis for a criminal case. Once a company declares the breach “closed,” that window has shut. Stan draws a sharp line between an intrusion, where criminals got in but took nothing, and an exfiltration, where sensitive data actually left the building. Only exfiltration tends to justify opening a case, and the deciding factor is never company size. It is whether the data is sensitive enough, and the number of affected Dutch citizens large enough, to matter for society.
The hardest part of the episode is about paying ransoms. The advice of the Dutch police is unconditional: don’t pay. Not because it’s illegal, but because it doesn’t work. Criminals who promise to delete stolen data often keep copies and sell them to other criminals or state actors later. A company that tells its customers “we paid, your data is safe” is, in Stan’s words, spreading fake news. And with resilient backups, the one practical reason to pay, getting your data back, has largely disappeared.
The lesson for security leaders is to decide in advance. How fast will you notify victims? Will you ever pay? Who is your regional high-tech crime contact? Decisions made under pressure in the first hours of a breach are the ones companies most often get wrong.
Get your Hacker T-shirt
Join the treasure hunt!
Find the code within this episode and receive your own hacker t-shirt for free.
