How a 19-Year-Old Hacked the NEWS Without Breaking In
Find Threat Talks on


Your Outlook account recovery will accept an authenticator code on its own.
No password, no inbox, no phone number. Whoever holds that TOTP secret owns the account, and the second factor you bought to survive credential theft becomes the only thing in the way.
Koen Kandelaars found one sitting in a PDF on a public help page at the NOS, the largest news organization in the Netherlands. He is 19, studies in Eindhoven, hunts vulnerabilities in his free time, and is an ambassador of HackShield. He scanned the QR code out of an onboarding manual in the middle of the night, then stared at his authenticator app for ten seconds because he could not believe it had worked. Rob Maas, Field CTO at ON2IT, walks the whole chain with the attacker himself: eleven findings in the first responsible disclosure, and a twelfth that Koen estimates at 1 to 5 million euros.
What you’ll learn
- Documentation is attack surface. A default endpoint served an internal onboarding manual with no authentication in front of it.
- Recovery undoes MFA. Outlook lets you reset a password using the authenticator code alone, collapsing two factors into one.
- What a good disclosure response looks like. NOS fixed it overnight and answered with a certificate and a handwritten note from the CISO.
Your cybersecurity experts
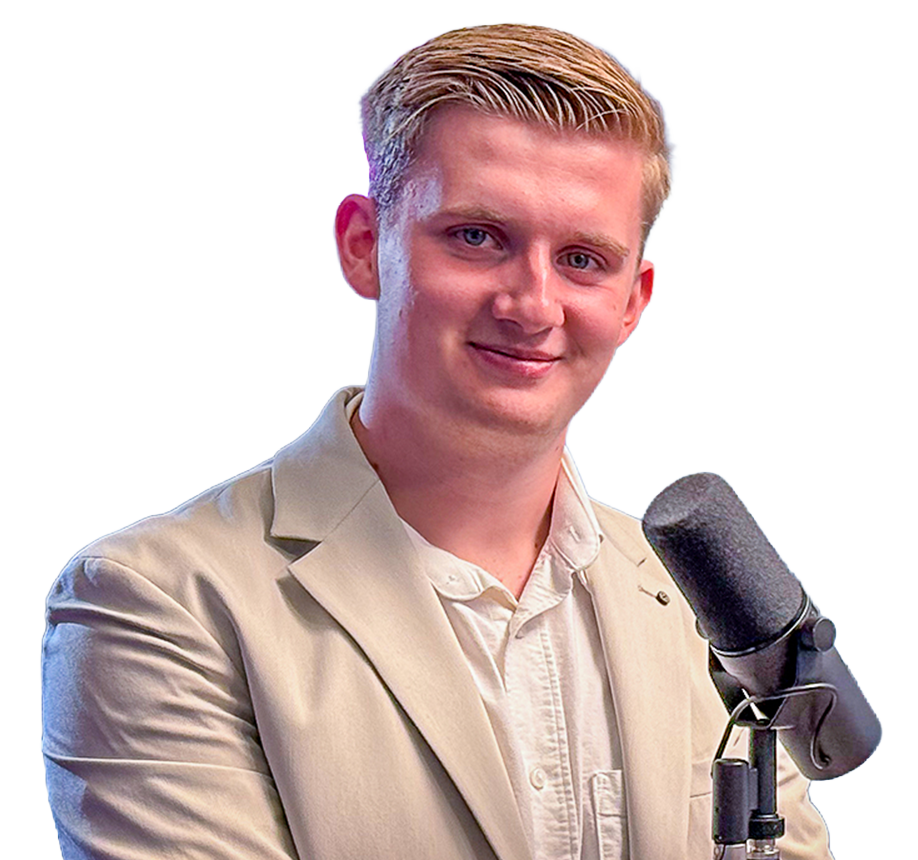
Koen Kandelaars
Student & Hackshield Embassador
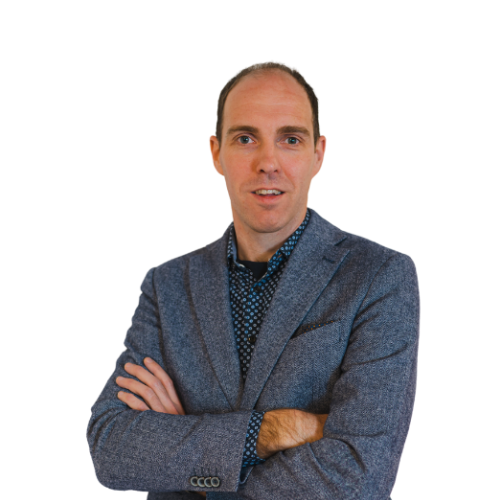
Rob Maas
Field CTO ON2IT
Episode details
The interesting thing about this attack is that nothing in it was clever. Koen mapped the NOS estate the way anyone would: domains, subdomains, where they resolve, what sits behind a WAF, what is hosted locally, and which systems look like nobody has updated them in a while. He then walked to a default endpoint that exists on that product by design, /users/help, and a PDF downloaded. There was no exploit. There was an ordinary page that had never been asked whether it should be public.
What that PDF contained is the part worth taking into your own environment. It was an onboarding manual explaining how to connect an authenticator app to an Outlook account, and the walkthrough screenshot inside it was a working TOTP QR code, complete with the owner’s email address encoded in it. Scanning it gave Koen a live second factor for a real project engineer. Nobody had classified a help document as a secret, because nobody thinks of documentation as something that holds credentials.
Then Microsoft finishes the job. If you tell Outlook you have forgotten your password, have no access to your email, and have no access to your phone number, it will let you recover the account on the authenticator code alone. Rob’s line in the episode is the one to remember: at that point there is no multi-factor authentication anymore, your TOTP is your only factor. The control the organization bought to make a stolen password worthless had become the single thing standing between an outsider and the account.
Koen stopped there, and he is explicit about why: resetting the password would have locked out the engineer, and logging into an account that is not yours is illegal regardless of intent, which he notes is not provable in court. What follows is the part more organizations should copy. NOS ran a plainly worded disclosure page, replied fast, remediated overnight, and sent a certificate, an invitation to their head office, and a handwritten note from the CISO. Rob’s closing framing is the one to keep: a simple human mistake with severe consequences, handled the way it should be handled. Koen’s own recommendation for the fix is equally unglamorous. The VPN was already there. Put the rest behind it.
Get your Hacker T-shirt
Join the treasure hunt!
Find the code within this episode and receive your own hacker t-shirt for free.
